
From exposed asset to prioritized finding — without waiting for the next annual test.
AI-powered offensive security · Europe & MENA
Find the gap
before an
attacker does.
Start with AI penetration testing and advance to manual testing, private bug bounty and red teaming; one offensive-security platform, backed by real human expertise.


7yrs
OFFENSIVE-SECURITY EXPERIENCE
2800
ASSESSMENTS COMPLETED
650
CRITICAL FINDINGS DISCOVERED
2
REGIONS — EUROPE & MENA
100%
HUMAN-VALIDATED WHEN SCOPED
The problem
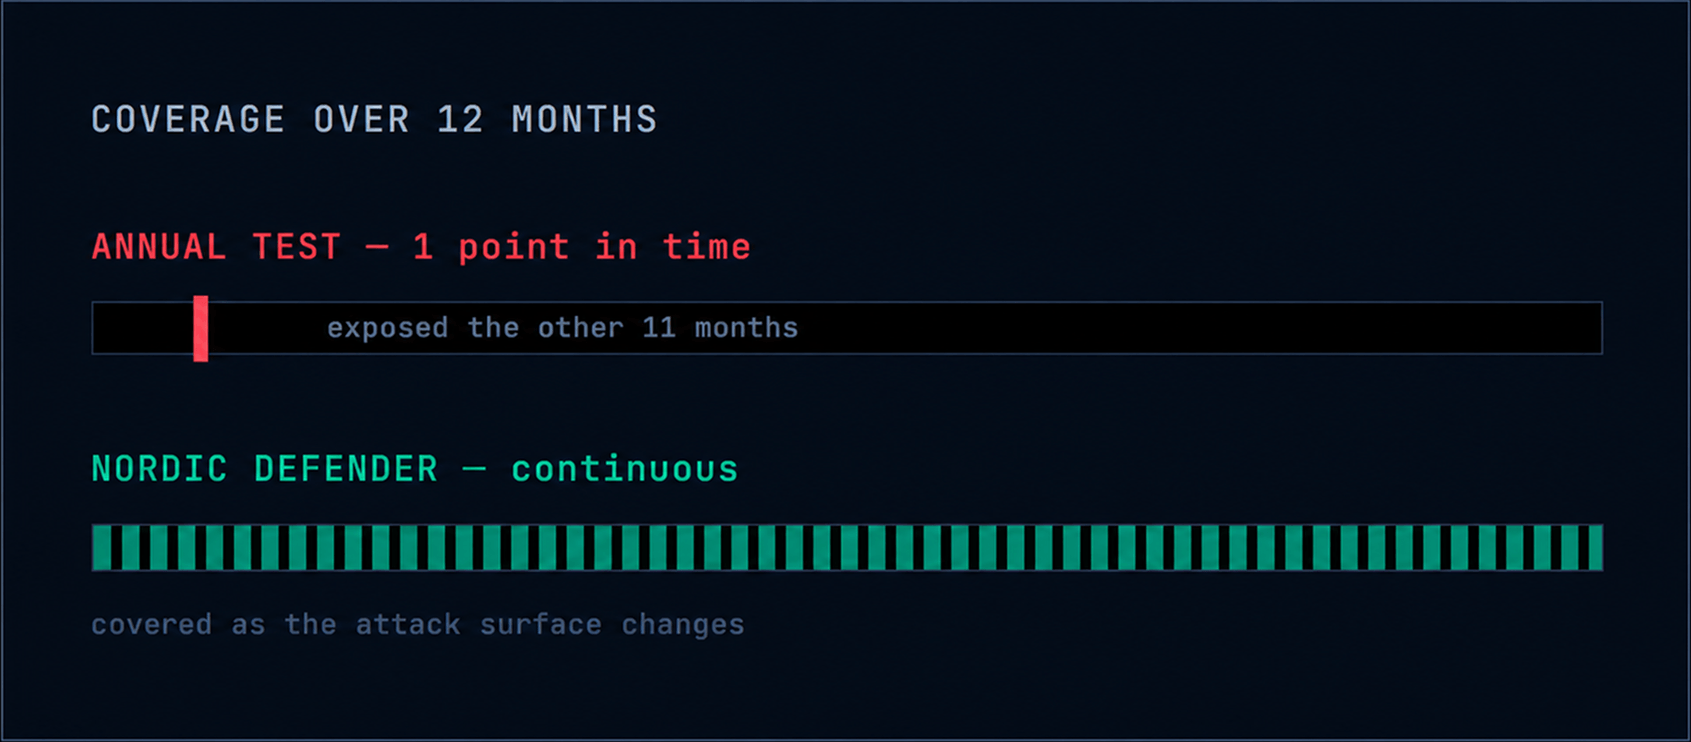
A test once a year leaves eleven months of gaps.
Your attack surface changes weekly. Attackers need one weakness on one unwatched day; continuous, human-validated testing closes that window.
The real platform
From exposure to prioritized action—fast enough to matter.
One operational workflow: discover exposure, validate what matters, prioritize remediation, track the result.
Nordic Defender
· offensive-security platform
live
Offensive Security Dashboard
Intelligence Scanning
Next-Gen Pen Test
Managed Bug Bounty
Submissions
Triage Room
Approved
Patched
Re-Test
Resolved
Submitted Vulnerabilities
ⓘ
7
None
41
Low
18
Medium
9
High
3
Critical
Platform demonstration data
Faithful reconstruction
01
Discover
Identify exposed assets, services and potential attack paths.
02
Test
Run AI-powered penetration testing against the authorized scope.
03
Triage
Separate valid findings from duplicates, rejected submissions and non-applicable results.
04
Prioritize
Connect technical severity to operational and business impact.
05
Remediate & Retest
Track remediation and confirm whether the exposure has been closed.
Speed changes the outcome
The finding only matters
if it reaches you in time.
Point-in-time testing goes stale. Specter shortens the distance from exposure to action.
>>>>>
The offensive-security maturity model
Start where you are.
Advance as your security matures.
Begin where you fit today and grow into the rest. One platform; you never change vendors.
Accessible · automatedAdversarial · resilience
Not sure where to start?
Answer four questions. We'll recommend the right first offensive-security level — no contact details required to see it.
See the platform in action
Watch offensive security run.
Moderation & Triage
How Nordic Defender Verifies Every Finding
Analytics & Insights Reporting Engine
How findings become severity reporting and prioritised action.
From Finding to Fixed
The Reporting & Analytics Engine | Nordic Defender
Why Nordic Defender
Not another AI scanner.
Seven years of real hunting.
AI brings speed and scale. Our experts add context and validate what matters.
AI Speed
Continuous and repeatable testing across exposed assets.
Human Validation
All findings will be reviewed for context and real-world impact.
Offensive Methodology
Attacker-style testing that chains weaknesses together, not a checklist scan for known issues.
Actionable Output
Security and leadership teams receive clear priorities, evidence and remediation direction.
Trust & evidence
Proof built over seven years.
The platform is new. The experience behind it is not. Here is the evidence.
~7yrs
NORDIC DELIVERY
2100
CLIENT ENGAGEMENTS
2800
ASSESSMENTS COMPLETED
250
NORDIC CLIENTS SERVED
820
COMPLETED RETESTS
REAL CLIENT SATISFACTION
“
We have enjoyed the service from Nordic Defender and are looking forward to continuing with their service in coming releases. The initial test has been very helpful to strengthen our knowledge about cybersecurity, and the close contact with the testers and project manager has been very valuable. We also appreciate the portal application where all issues are reported with great details.
Ylva Mendes
Software Developer — Vitec Software
Sweden / Nordics · Offensive-security testing
“
This is what I love: The process of continuous pentest, instead of one or twice per year testing; pentest is now part of the monthly process. The portal where we can follow the findings and integrate security issues into Jira and the team’s daily work. The success manager that helps us in the process.
Anders Klintelius
Chief Technology Officer - Stratsys
Nordics · Offensive-security testing
“
Nordic Defender is a great choice for pentest as a service vendor. The engagement has improved our focus on security testing with a new agile approach and a platform that provides great insight into our pentest vulnerability and cost management. Nordic Defender is a partner of choice.
Morten Eriksen
Group Security Advisor - EcoOnline
Sweden / Nordics · Offensive-security testing
Frequently asked questions
Before you decide.
Compliance
Jan 19, 2025
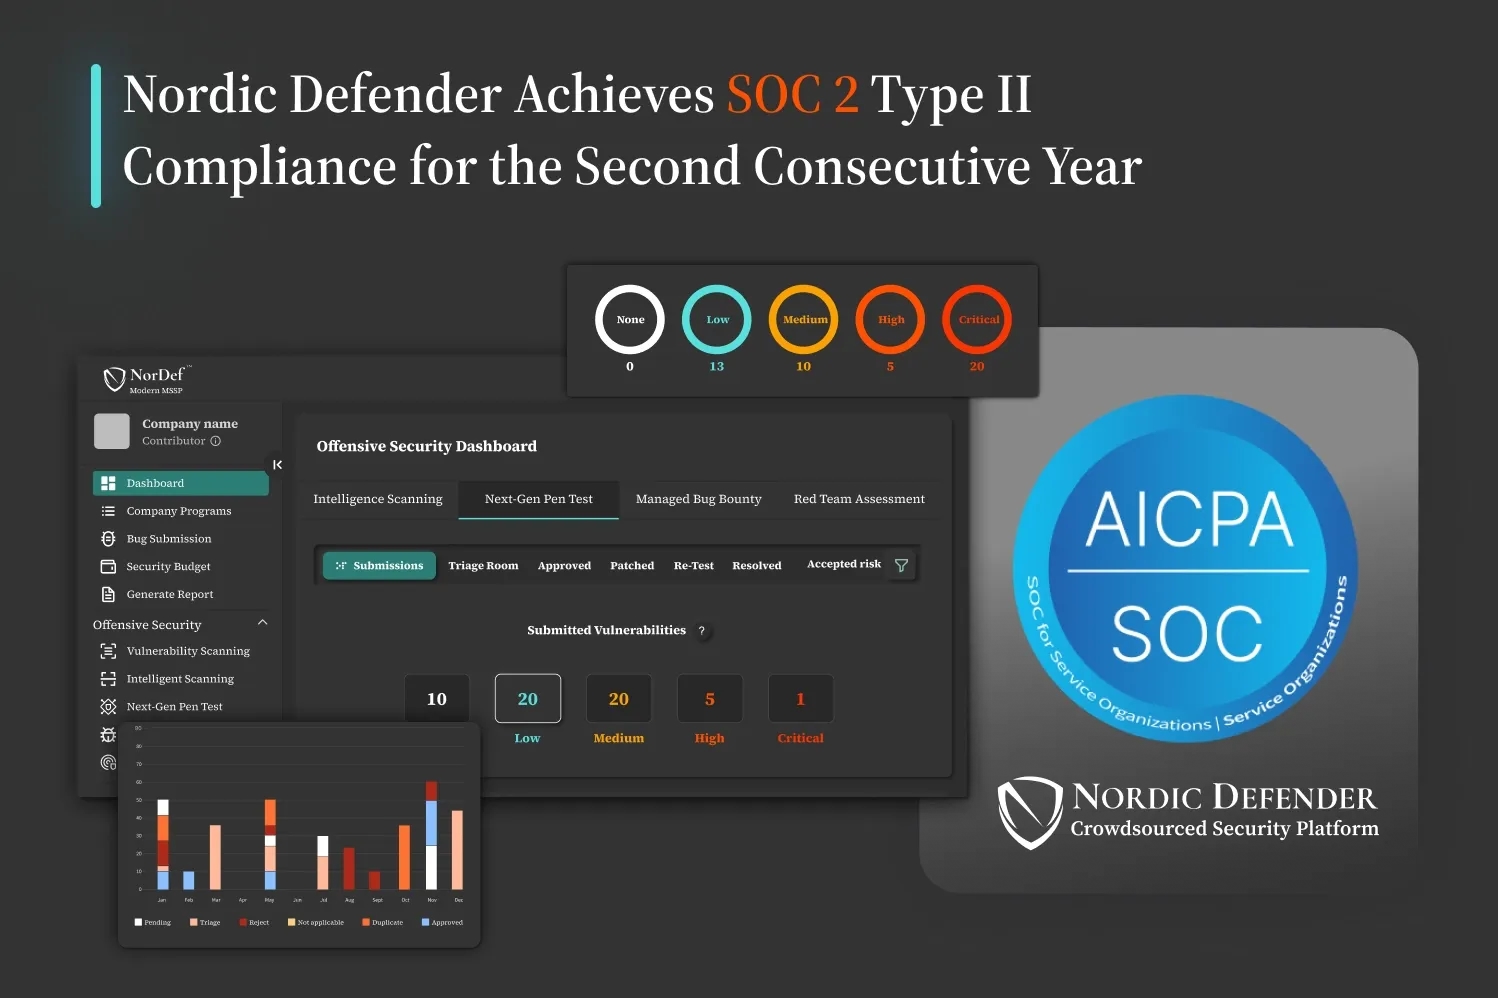
Nordic Defender achieves SOC 2 Type II compliance
Independent audit completed for the second year running.
Read article ↗
Company
Dec 10, 2024
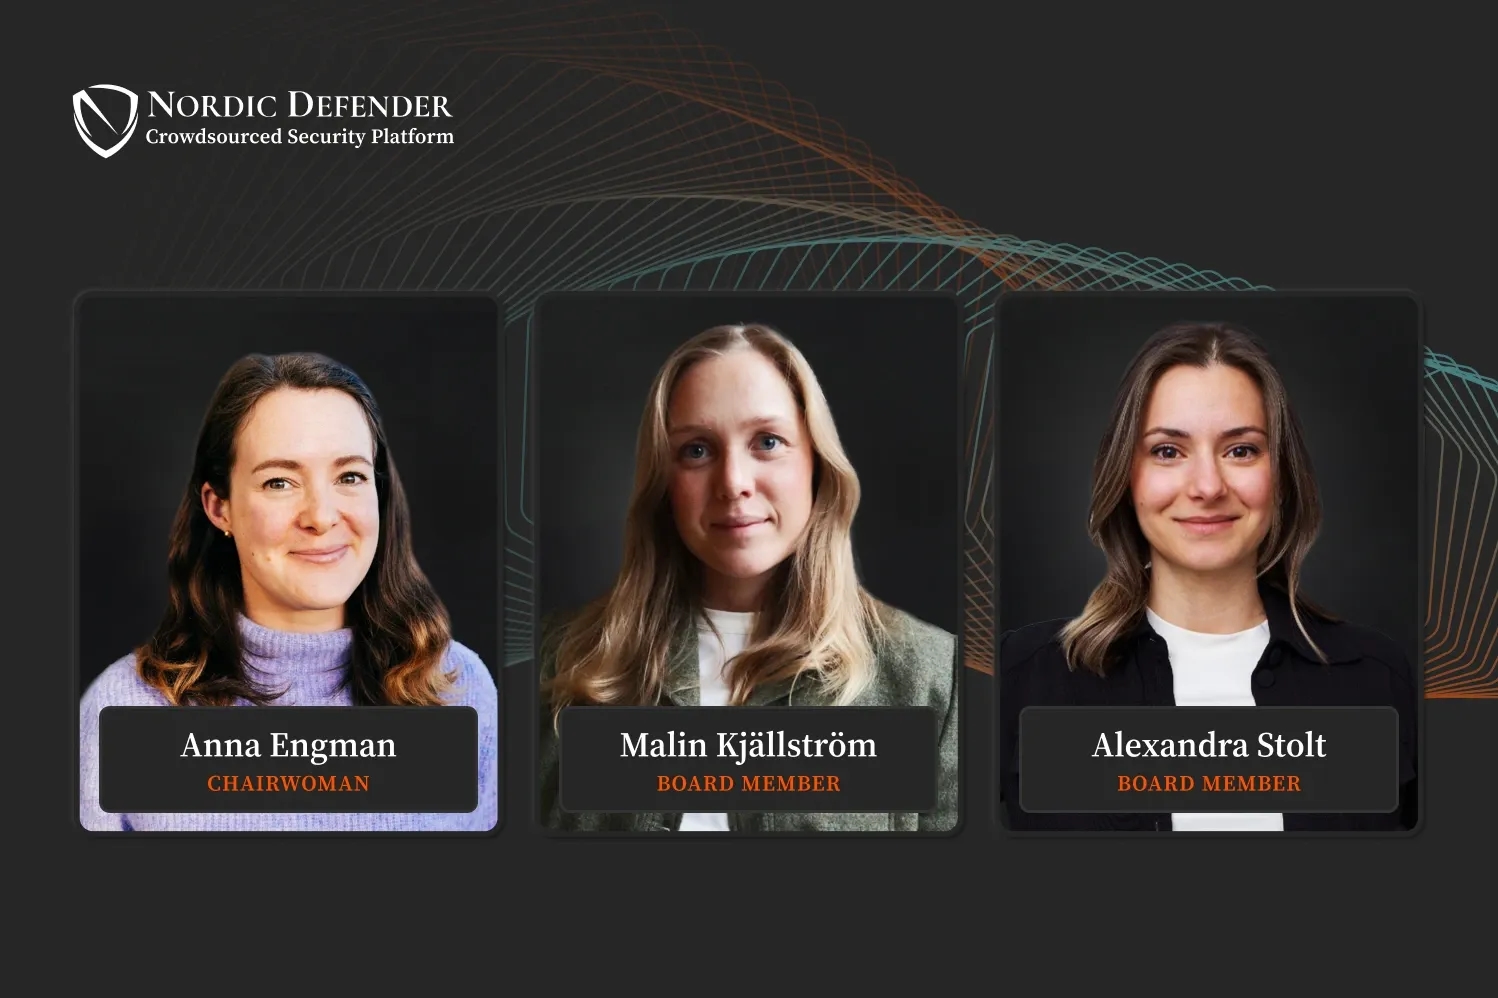
Welcoming new board members — Anna Engman as Chairwoman
Strengthening governance as we expand across Europe and MENA.
Read article ↗
Event
Oct 10, 2024
Reflections from Cybertech Europe 2024
Key takeaways from La Nuvola, Rome.
Read article ↗
Product
2026
Introducing Specter — AI penetration testing
AI speed with human offensive-security expertise.
Read article ↗
Specter is new. The expertise behind it is not.
New AI capability.
Seven years of Nordic offensive-security
experience.
Built for the speed of today's attack surface.